
30 days with Claude Mythos Preview: How Tenable adapted our security program, and why yours is next
AI Summary
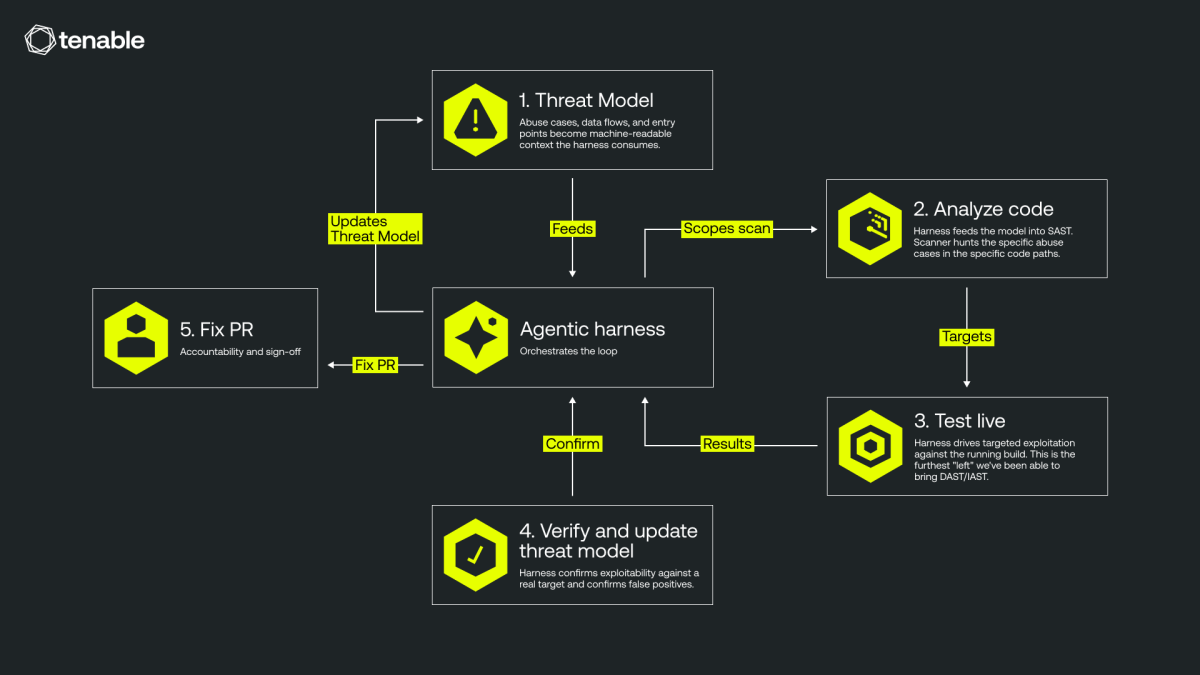
Tenable spent 30 days running frontier AI models against our own code. It didn’t just find bugs — it proved they’re real, with reproducible exploits. That fundamentally changes code security from ranking potential code defects to a much higher signal focused on the findings that matter.
Discussion
Sign in to join the discussion.
Loading comments…