
Reduce supply chain risk with SBOM-based dependency scanning
AI Summary
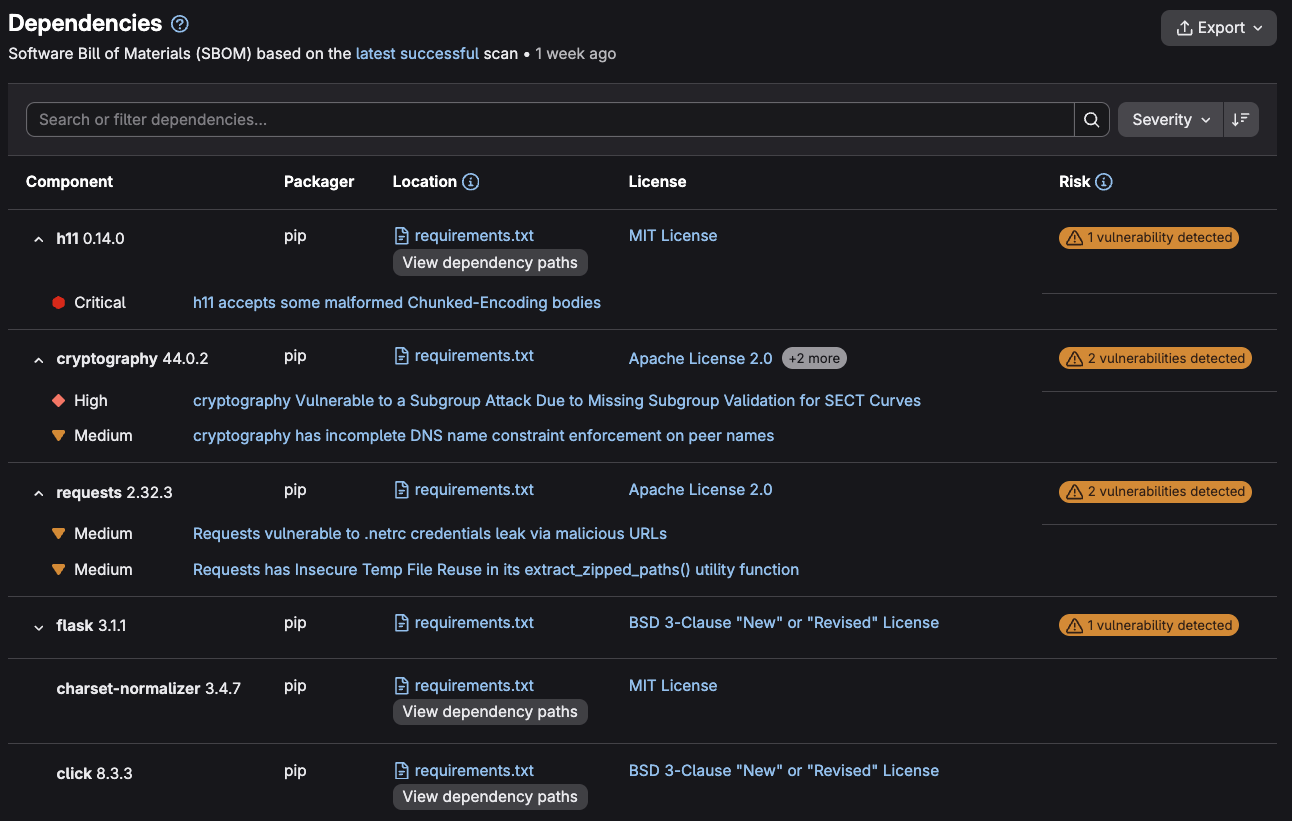
Third-party code dominates most codebases, and four recent supply chain incidents show how a single compromised package can ripple into every project that depends on it. AI is compounding this problem: Research suggests nearly half of AI-generated code contains vulnerabilities . Traditional dependency scanners, including GitLab's Gemnasium analyzer, were engineered to answer one question: Which of my declared packages have known CVEs?
Discussion
Sign in to join the discussion.
Loading comments…