
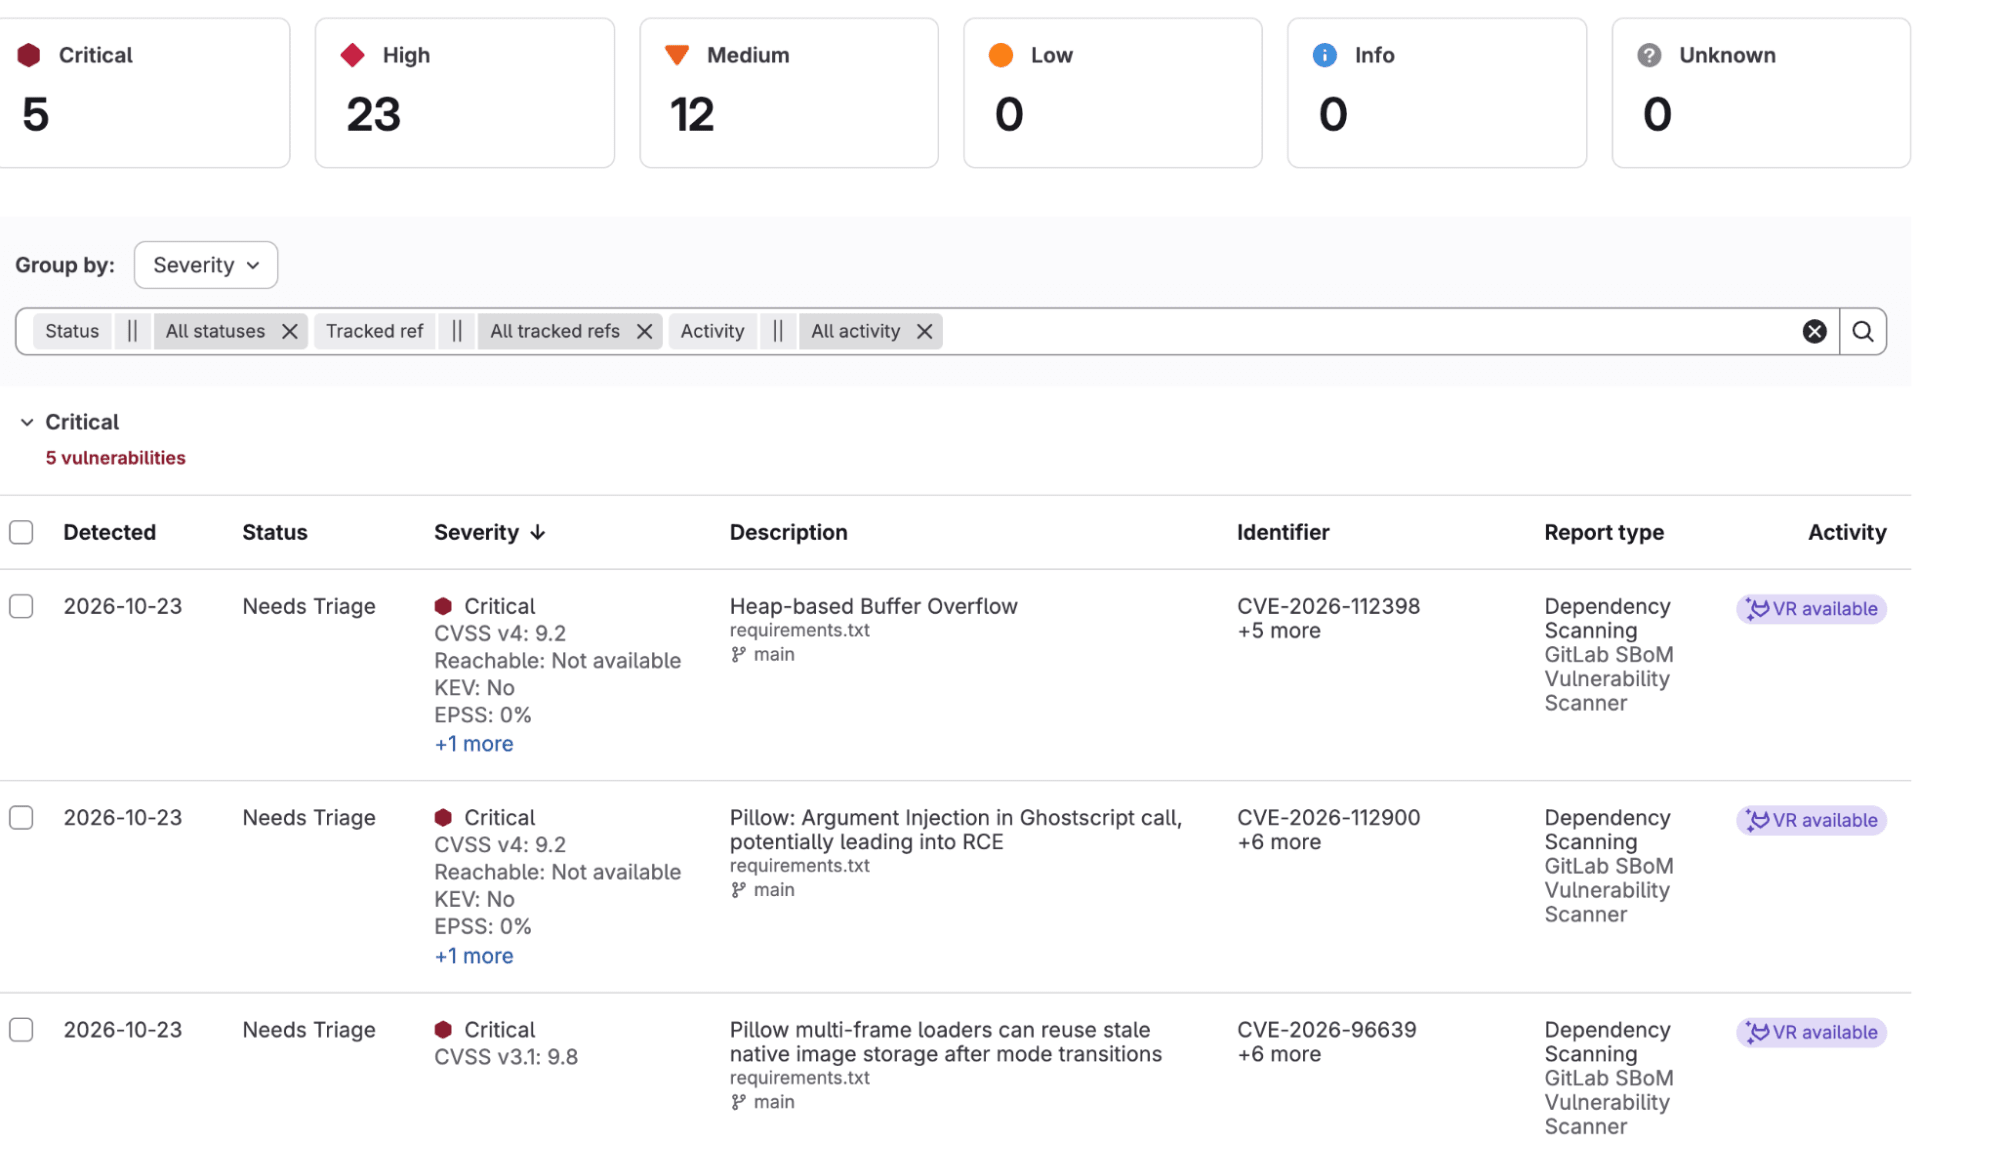
Pillow CVE-2026-112900: How to find and fix it with GitLab
AI Summary
GitLab is not affected by CVE-2026-112900 or the other vulnerabilities fixed in Pillow 13.0.0. GitLab products do not include the Pillow library, and our Security team has found no evidence of impact to GitLab-managed infrastructure. GitLab.com, GitLab Self-Managed, and GitLab Dedicated are not impacted.
Discussion
Sign in to join the discussion.
Loading comments…