
Uncover the business logic vulnerabilities SAST scanners miss
AI Summary
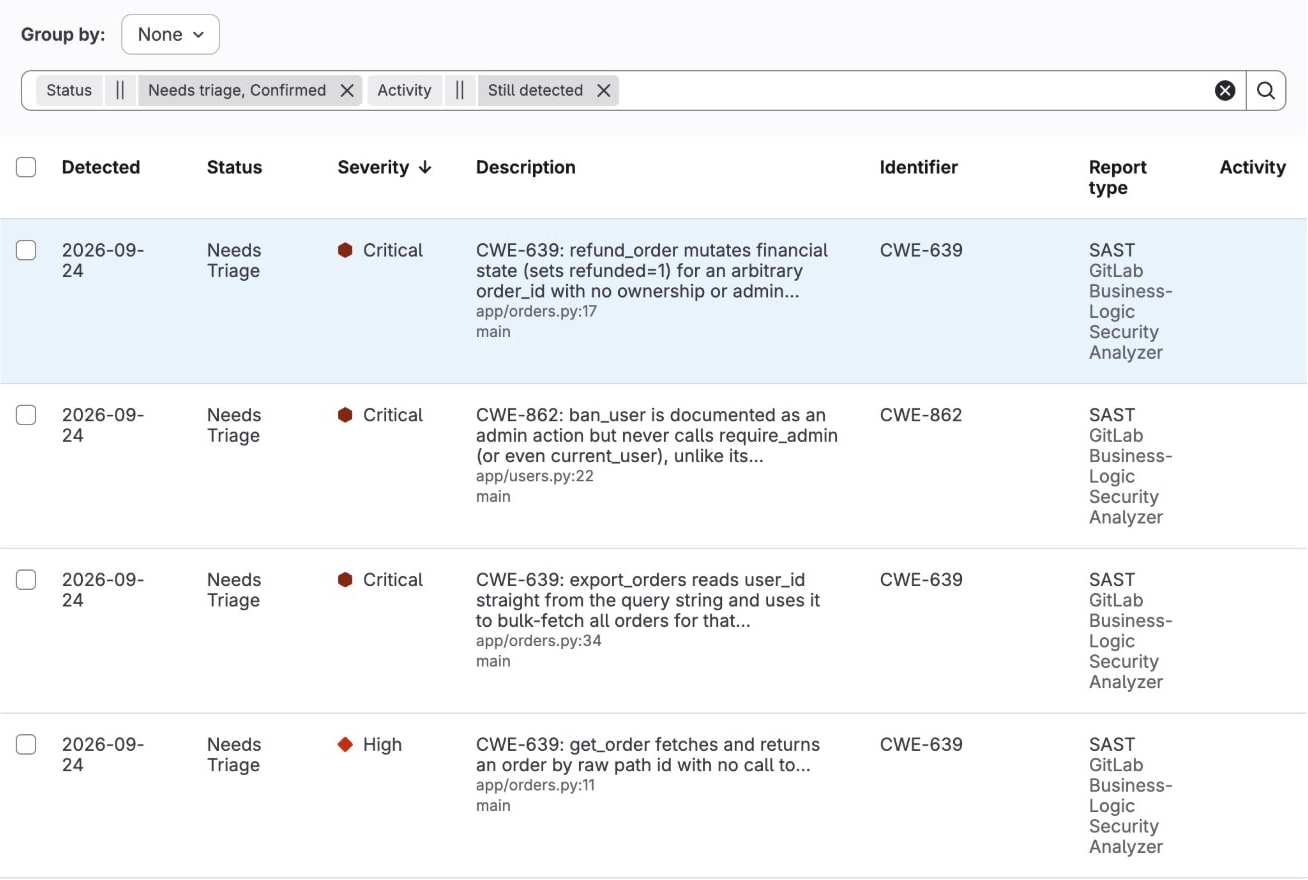
Broken object-level authorization ranks first on the OWASP API Security Top 10 , and OWASP says that traditional static application security testing (SAST) tools struggle to find access control flaws. A missing authorization check is an absence of code, so a scanner that matches patterns has nothing to match. You can find the gap only if you already know what the endpoint is meant to enforce.
Discussion
Sign in to join the discussion.
Loading comments…