
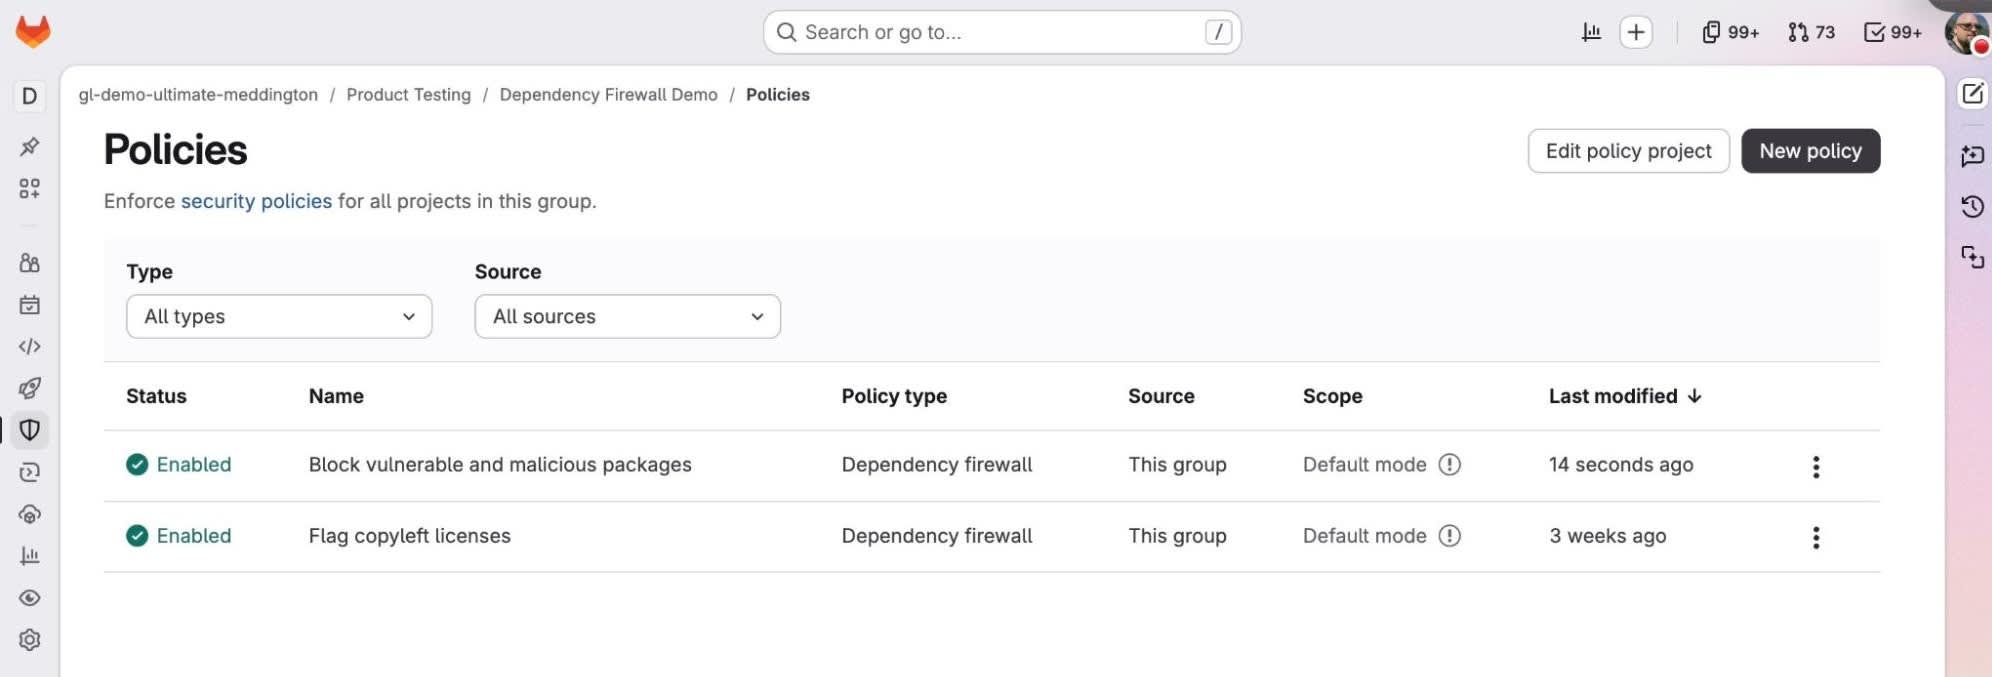
Dependency Firewall: Block risky packages before the build
AI Summary
Malicious packages could turn up in the public registries your builds depend on. Increasingly, the developer is not the one choosing what gets pulled in because AI coding agents now add open source dependencies on their own, often without anyone reviewing or even seeing what landed in the build. That combination means a malicious or vulnerable package can enter your build without anyone deciding to allow it.
Discussion
Sign in to join the discussion.
Loading comments…